THREATMON · PARTNER AND ONLY RESELLER IN POLAND

THREATMON IN POLAND

A threat intelligence platform that shows your company the way an attacker sees it: leaked passwords, lookalike domains, vulnerable servers and dark web chatter about you. In Poland, it is available only through Jet Lark.

01

WHAT THREATMON IS

ThreatMon is a SaaS cyber threat intelligence platform. Nothing is installed in your network — it watches your organisation from the outside: internet-facing assets, the dark web, social media, app stores and suppliers. Every finding lands in one console as an alert with a risk rating.

Instead of separate tools for attack surface scanning, leak monitoring, brand protection and supplier assessment, you get one platform and one priority list, ordered by AI across all modules at once.

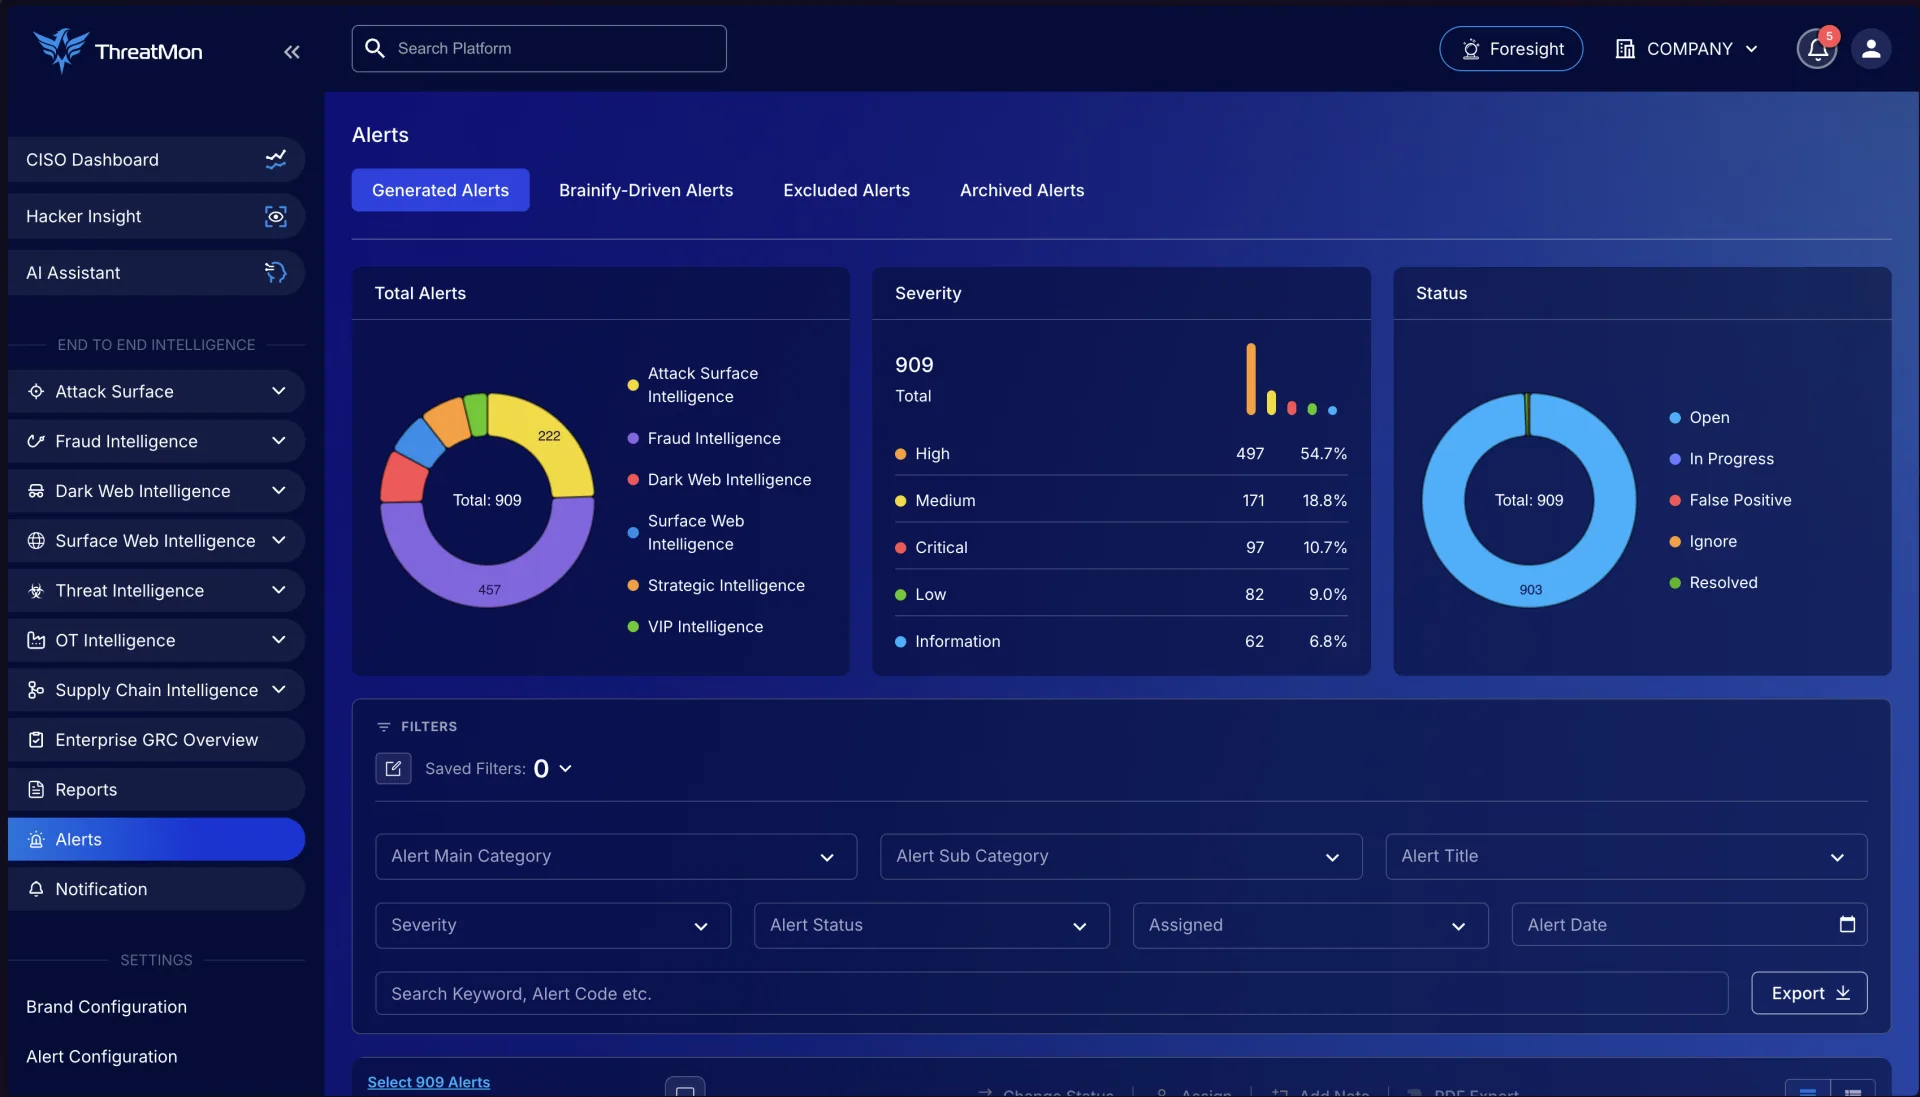
ThreatMon alerts panel: 909 alerts broken down by module, severity and status
JET LARK × THREATMON

Jet Lark is a ThreatMon partner and the only reseller of the platform in Poland. We run the call and the trial account, prepare the quote and invoice as a Polish company. If you want ThreatMon connected to your SIEM, SOAR or ticketing system, we do it together with your team.

150M+STEALER LOGS
550K+PHISHING SITES DETECTED
300K+RANSOMWARE ATTACKS ON RECORD
130+APT GROUPS TRACKED
15K+HACKED WEBSITES
300+ALERT CATEGORIES

SOURCE: THREATMON.IO, OCTOBER 2026

See what ThreatMon finds about you

A free full-access trial account — the platform starts monitoring your domains straight away.

02

PLATFORM MODULES

Modules can be bought separately or together. Each one feeds a shared risk score, so even with a single module your alerts are ordered by importance, not by the order they arrived in.

Module 01Attack Surface Intelligence

Everything you expose to the internet — including what nobody remembers

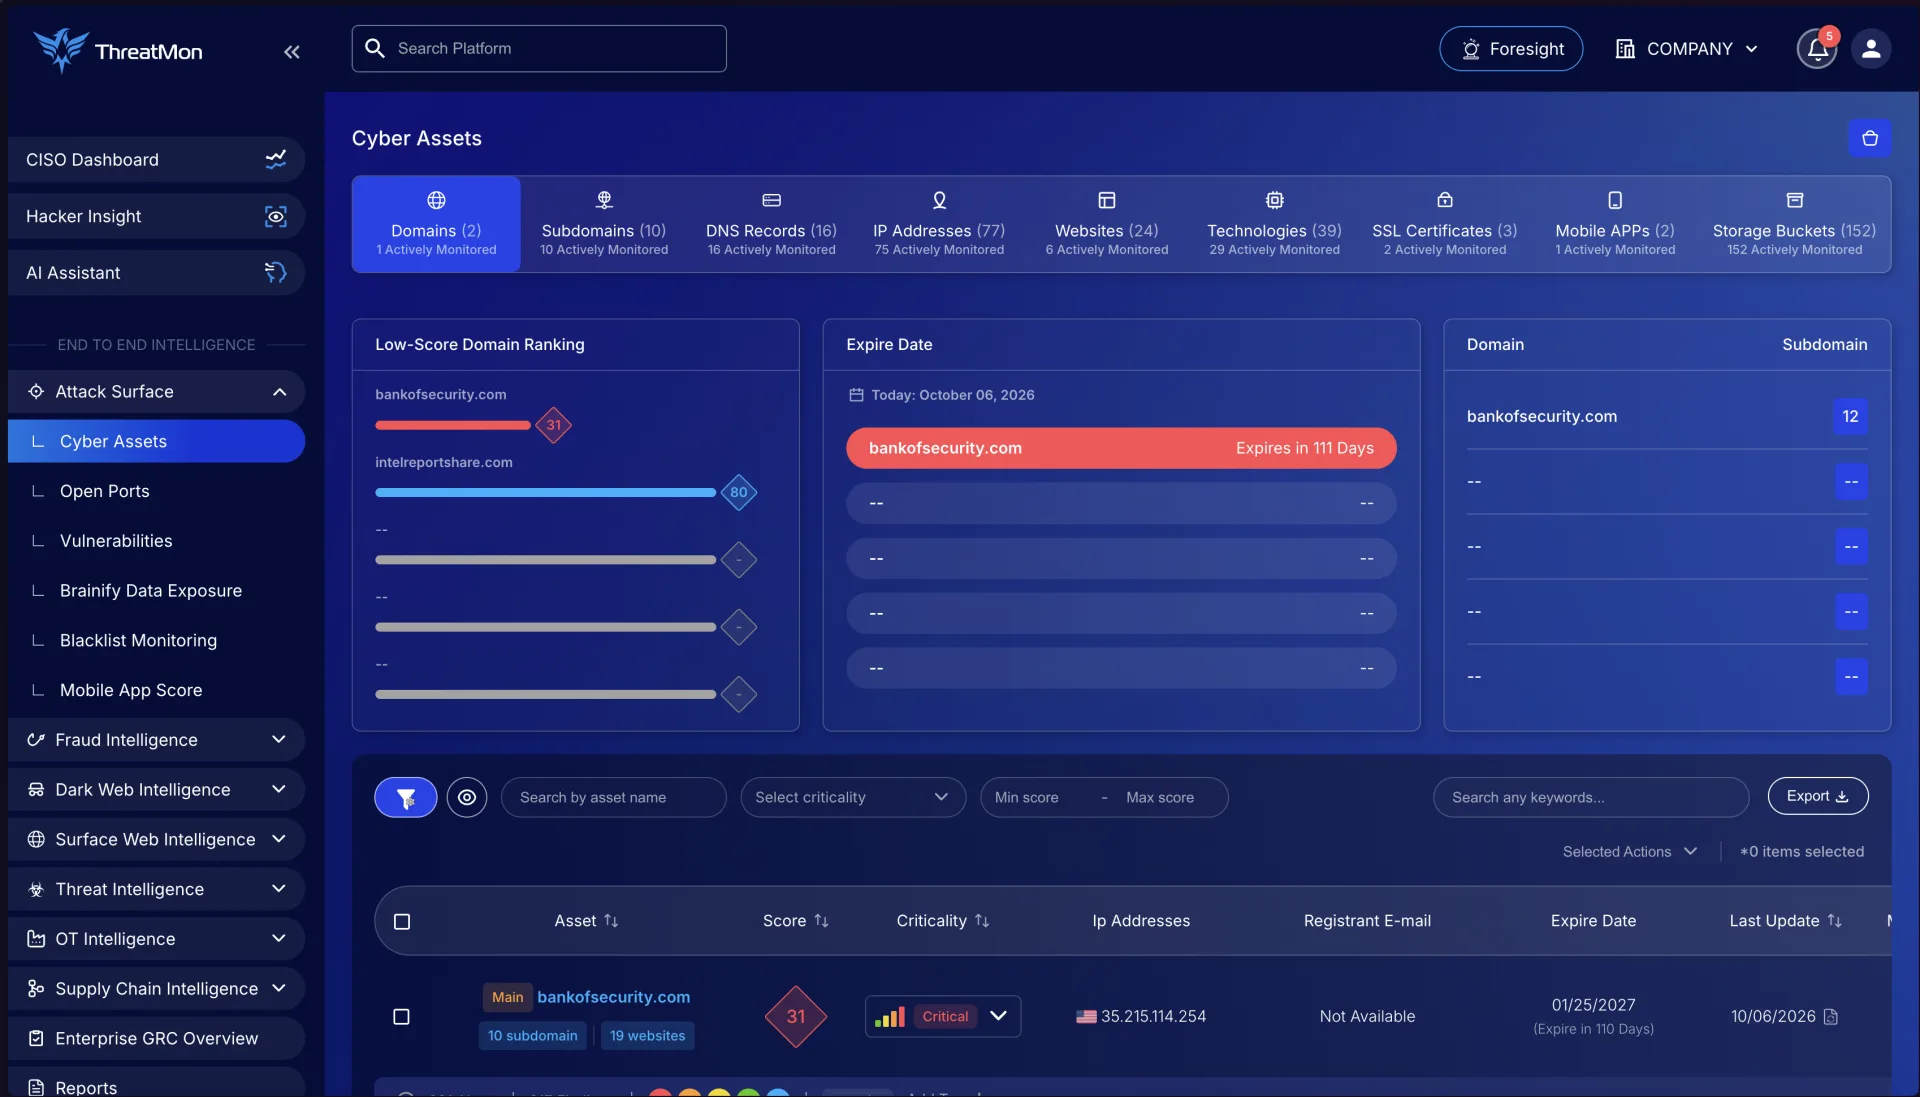
The platform discovers domains, subdomains, IP addresses and services belonging to the company, its subsidiaries and suppliers, then keeps watching them. It flags misconfigurations, known vulnerabilities in detected technologies and blacklisting. Continuous external pentesting probes web assets from an attacker's point of view.

  • Asset inventory
  • Misconfigurations
  • Vulnerabilities
  • Mobile app security
  • IP and domain blacklists
  • Continuous external pentest
ThreatMon Attack Surface: discovered domains, subdomains, IP addresses, certificates and mobile apps
Module 02Dark Web Intelligence

Leaked passwords and company data, before someone uses them

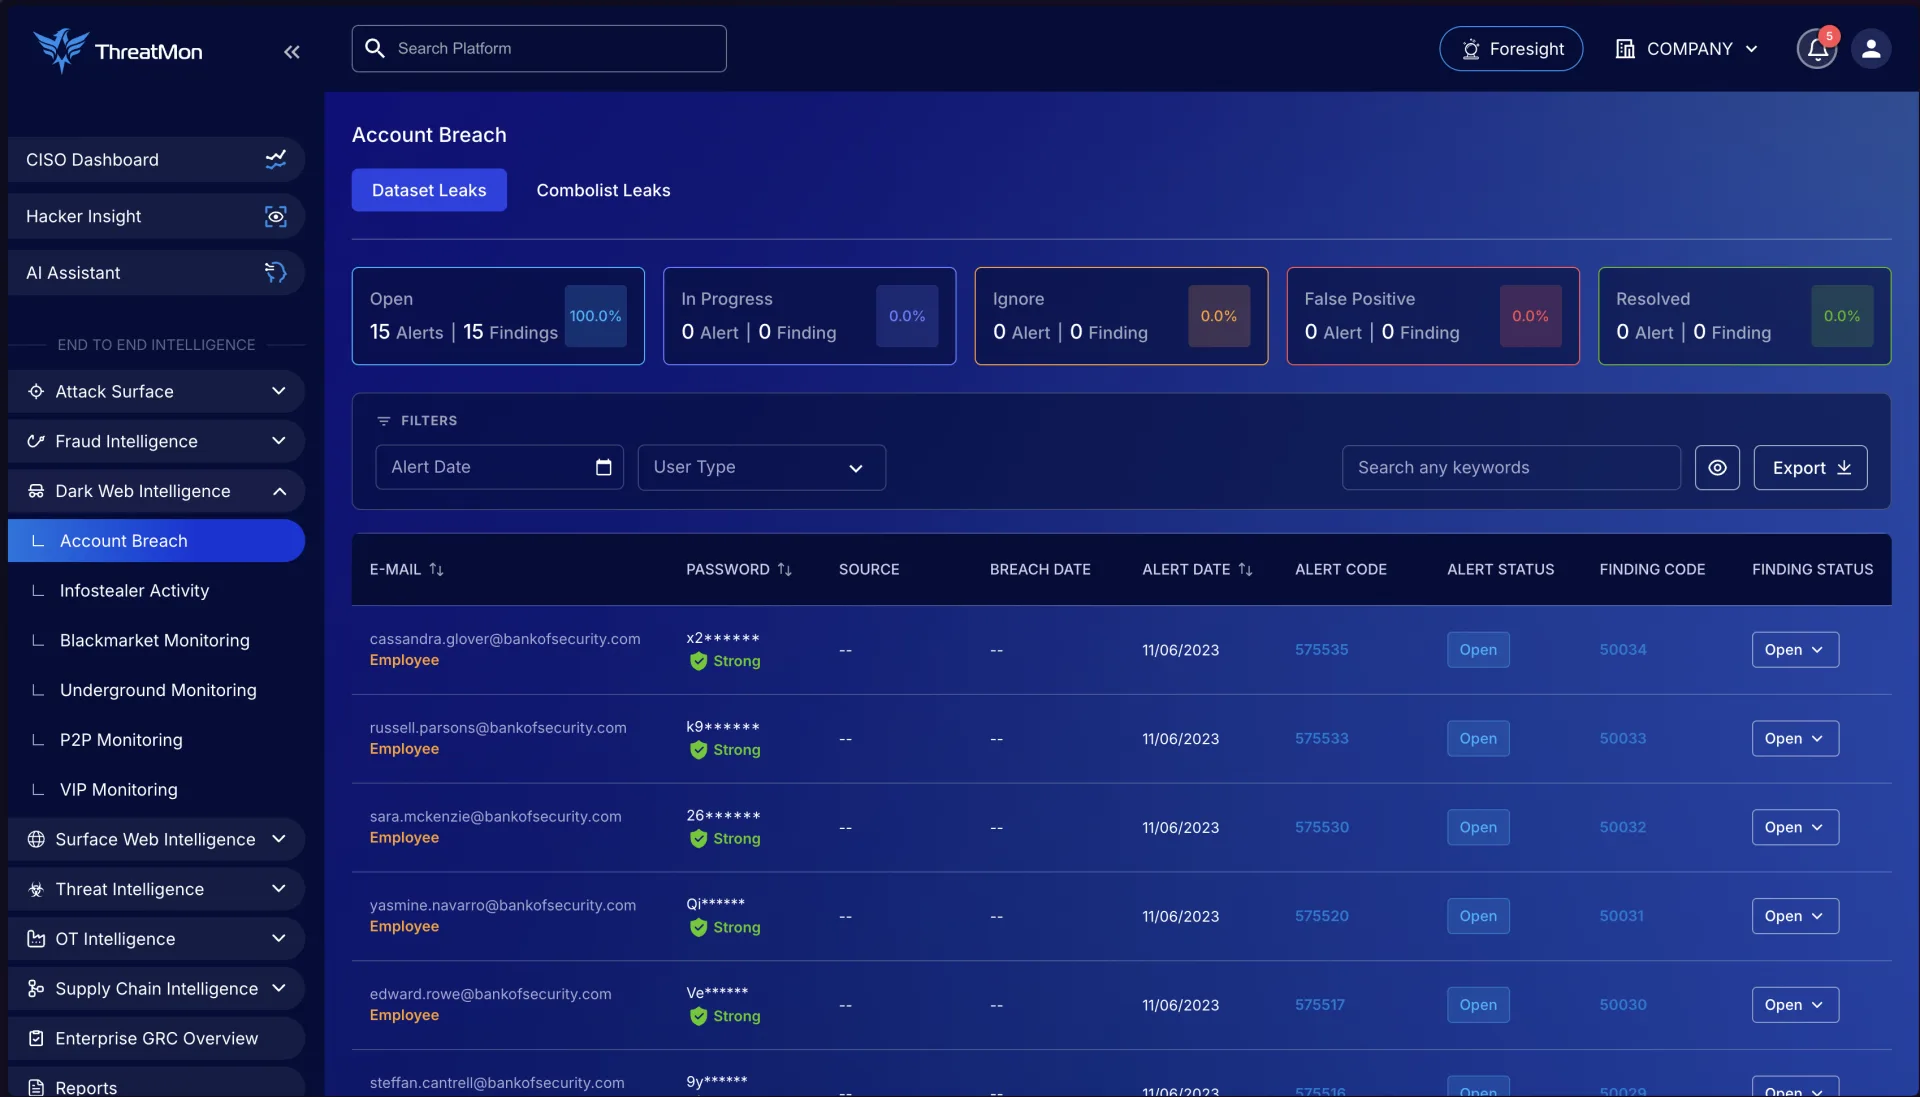
Monitoring of forums, black markets and hidden networks for your data. ThreatMon finds employee and customer logins in leaks and in stealer logs (malware that harvests passwords from browsers), listings selling company data and threads where hackers discuss your organisation. Results can be filtered by country and industry.

  • Leaked credentials
  • Stealer logs / botnets
  • Black markets
  • Hacker forums
  • Executive and VIP protection
ThreatMon Dark Web: leaked employee credentials with masked passwords
Module 03Fraud Intelligence

Fake domains, profiles, apps and ads using your brand

Detects phishing domains and campaigns impersonating the company, fake social media profiles, rogue apps in app stores and APK sites, ads abusing the brand and impersonation of executives. It also watches black markets for stolen payment card data.

  • Phishing
  • Social media
  • Rogue apps
  • Fake ads
  • Payment card data
  • Executive impersonation
Module 04Cyber Threat Intelligence

Who is targeting your industry, and how

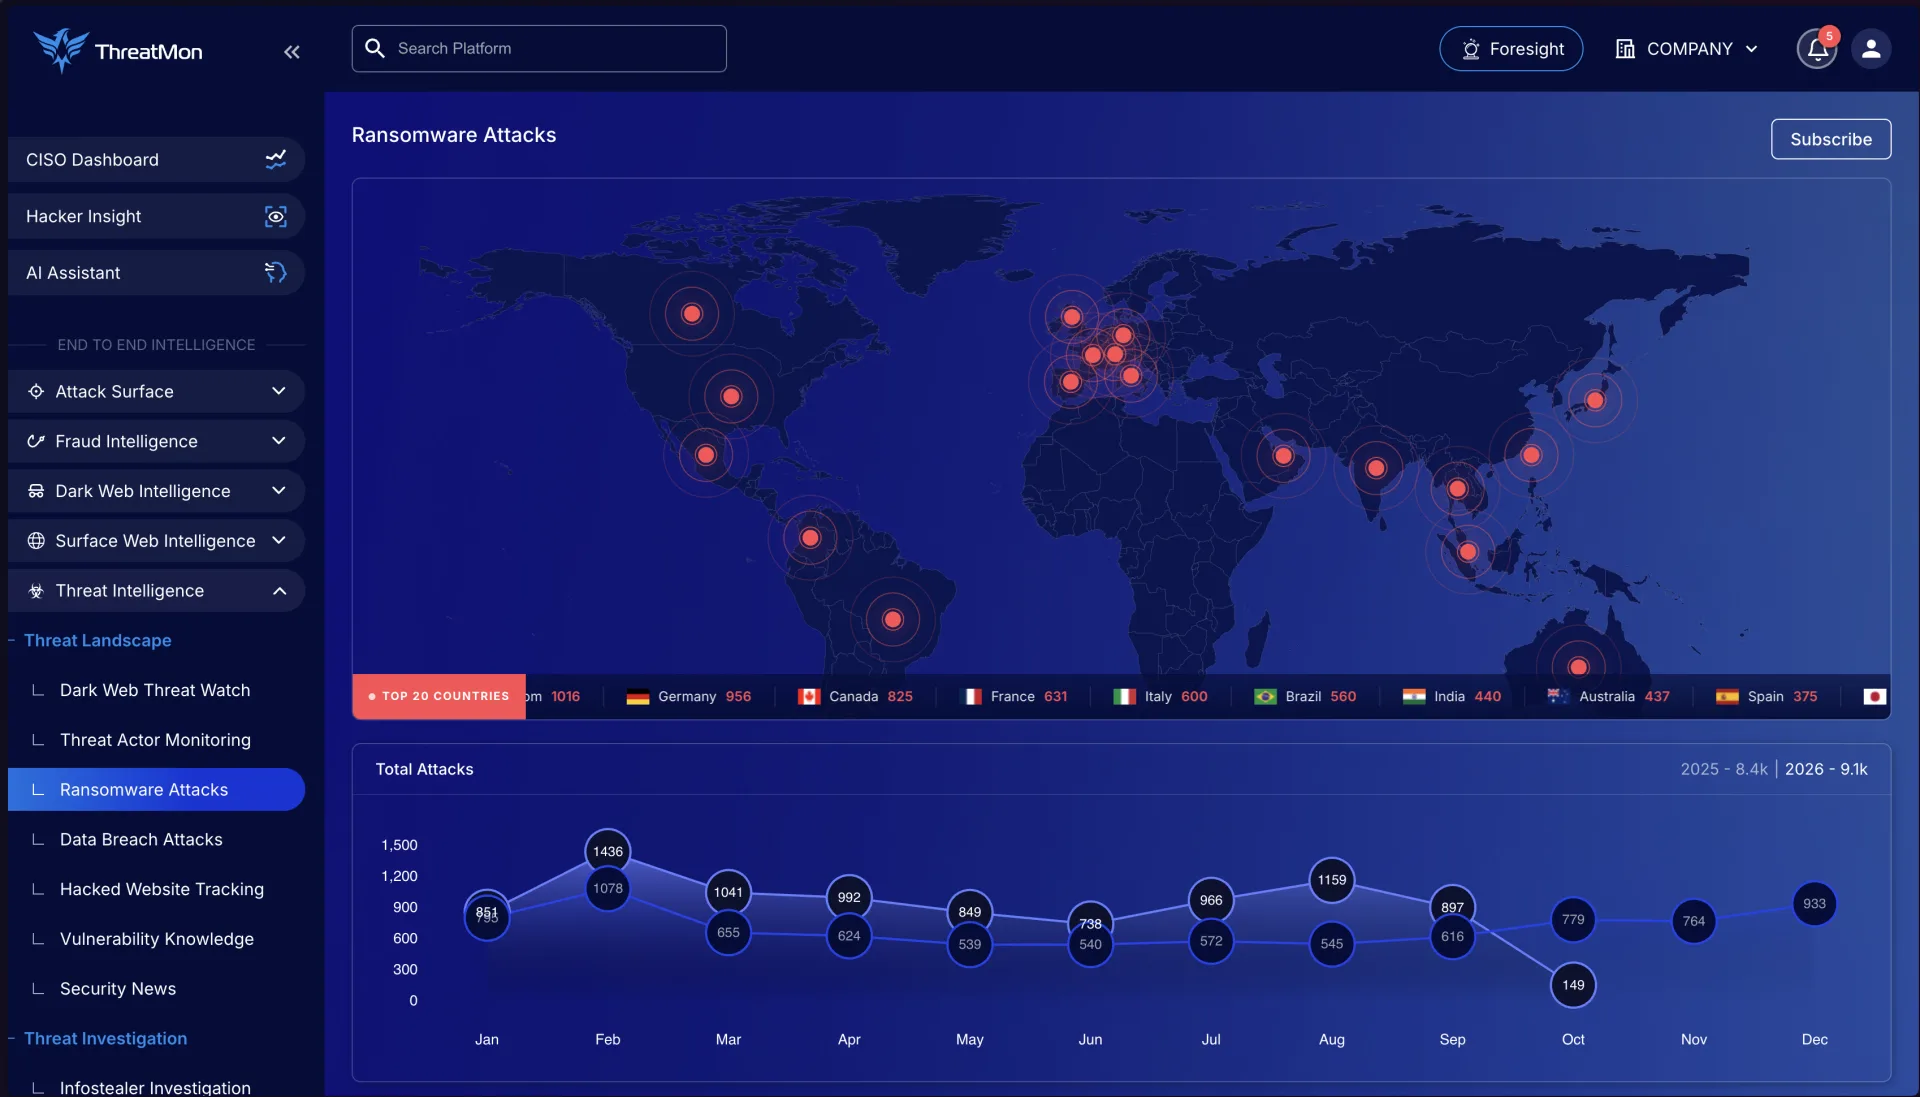
The core of the platform that ties the other modules together. It tracks APT groups and their tactics, ransomware activity in real time, database leaks and C2 infrastructure (the servers attackers use to control compromised machines). It aggregates feeds and indicators of compromise (IOCs) you can push to your own tools.

  • APT groups
  • Live ransomware
  • Database leaks
  • C2 detection
  • IOC feeds
ThreatMon Threat Intelligence: global ransomware attack map and monthly counts
Module 05Supply Chain Risk

Supplier risk without sending questionnaires

The same analysis you get for your own company, run against suppliers: their internet-facing assets, leaked credentials, authentication practices and application, network, DNS and SSL/TLS configuration. Each supplier is rated across nine security layers, and an audit-ready PDF report is one click away.

  • Supplier assets
  • Supplier leaks
  • Identity and access
  • 9-layer rating
  • PDF report
Module 06Brainify AI

A risk score and an AI assistant that tell you what to fix first

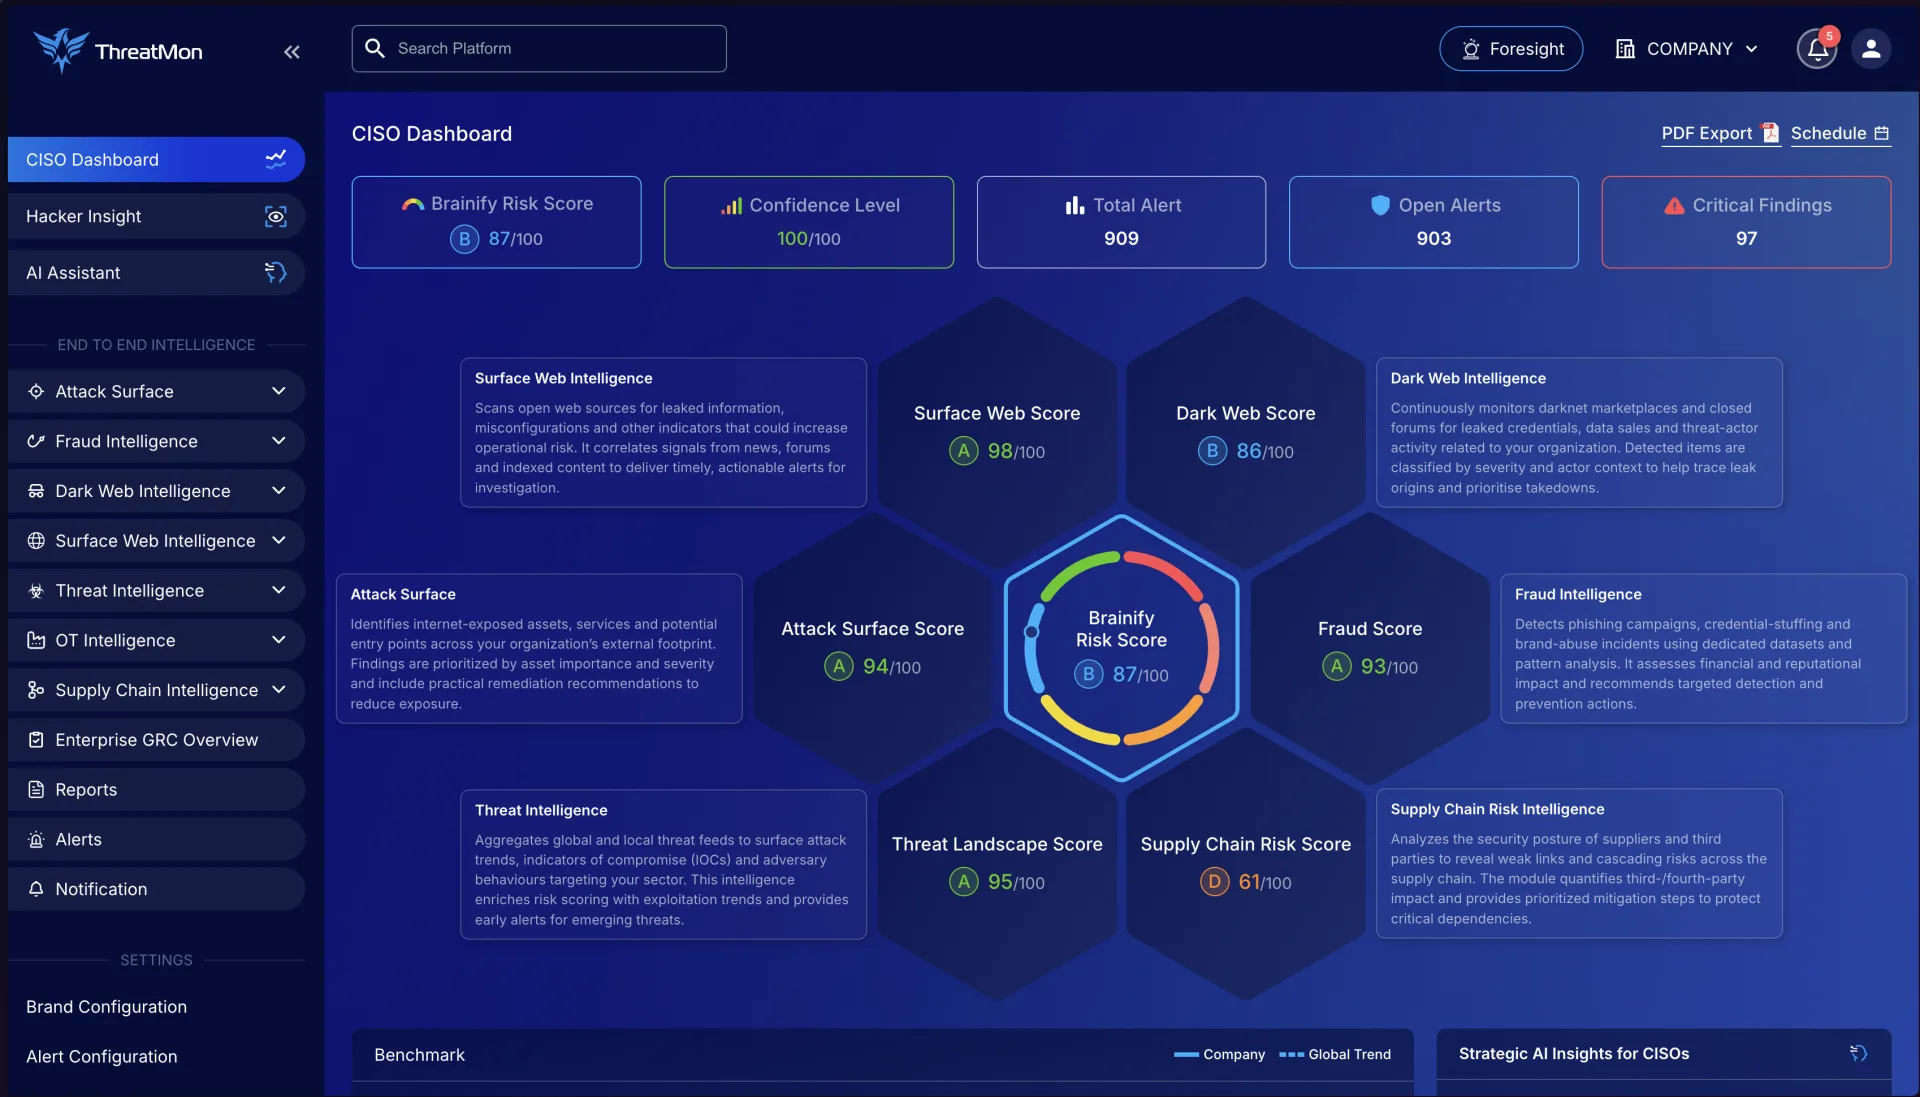
Brainify AI Risk Score combines data from every module into one risk rating that updates with each new alert and keeps its history. The ThreatMon AI assistant answers security questions in plain language, explains where a score comes from and helps decide the order of work.

  • AI risk score
  • Risk history
  • Alert prioritisation
  • AI assistant
ThreatMon CISO Dashboard: Brainify Risk Score and scores for every module
Try the modules on your data

The trial account monitors your own domains, so you see straight away what ThreatMon finds about you.

03

WHEN AN ALERT IS NOT ENOUGH

Spotting a fake domain or a leak is half the job. ThreatMon also offers operational services that close the case on the other side. Scope and availability are agreed in the quote.

01 · TAKEDOWN

Removing fake domains, profiles and apps

Reporting and pursuing the takedown of phishing sites, social media accounts and apps impersonating your brand.

02 · DARK WEB DATA REMOVAL

Removing data from the dark web

Locating and removing company data offered on black markets and forums — customer records, internal files, financial data — with follow-up monitoring.

03 · MALWARE ANALYSIS

Analysis of suspicious files

Sample analysis in an isolated environment, with a report on the attack vector and recommended next steps.

04 · PENTESTS AND RESPONSE

Penetration testing and incident response

External penetration tests, IoT/OT testing, ransomware risk assessment and, when an incident happens, response, digital forensics and continuity planning.

04

WHO IT IS FOR AND WHY

Security teams

The CISO gets a single risk score to report to the board. The SOC gets alerts with context and priority instead of raw data, and the incident response team learns who is behind an attack and what tools they use. In smaller companies without their own SOC, ThreatMon covers work there are no people for.

Industries under pressure

ThreatMon has ready-made scenarios for finance, healthcare, energy, manufacturing, retail and e-commerce, telecoms and government. For the public sector there is also a separate product — National Cyber Defence — built for CERTs and institutions responsible for cybersecurity at national level.

NIS2, KSC and DORA

Poland's amended National Cybersecurity System Act (KSC), which implements NIS2, has been in force since 3 April 2026. Entities in scope have until 3 April 2027 to put their risk management and security measures in place. The financial sector has applied DORA since January 2025.

ThreatMon helps with part of these obligations: continuous threat identification, vulnerability management, supplier risk assessment and reporting. It does not make you compliant on its own — that also takes procedures, people and documentation.

Try ThreatMon before your audit

See on your own data which KSC and DORA obligations the platform helps with — before you decide.

05

INTEGRATIONS

ThreatMon does not replace a SIEM or EDR — it looks outwards, they look inwards. So alerts and indicators of compromise go where your team already works.

SIEM

Microsoft Sentinel, Splunk, IBM QRadar, LogRhythm, AlienVault

SOAR

Cortex XSOAR (Palo Alto Networks), Siemplify

Firewall and network

Check Point, Palo Alto Networks, Fortinet, Cisco

EDR, email and more

CrowdStrike, McAfee, Proofpoint, Rapid7, Slack

LIST PER THREATMON.IO/INTEGRATION — WE CONFIRM SPECIFIC INTEGRATIONS IN THE QUOTE

Ask about integrations

Tell us which SIEM or SOAR you use — we will check the integration and include it in the quote.

06

CERTIFICATIONS AND AWARDS

CertificationsSecurity and quality

ISO/IEC 27001, ISO 9001, TX-RAMP and CSA STAR for AI Level 1 (Cloud Security Alliance, August 2026).

2026 awardsIndustry

Five-time Community Choice winner at the 2026 Cybersecurity Excellence Awards and a 2026 Global InfoSec Award from Cyber Defense Magazine.

CompanyVendor

More than 70 specialists and more than 150 customers. Offices in Newark (Delaware, USA) and Istanbul. The platform is reviewed on Gartner Peer Insights and G2.

07

HOW TO START

Step 1Call

We agree what to monitor

Domains, brands, executives, suppliers — and which of them are least watched today.

Step 2Trial account

Free access to the full platform, on your data

We set up the account and the platform starts monitoring your domains straight away. Real alerts instead of slides — and we help with setup and answer questions.

Step 3Quote

A licence sized to your assets

The price depends on the number of monitored assets and the modules chosen. Jet Lark issues the quote and the invoice.

08

FREQUENT QUESTIONS

Does ThreatMon need to be installed?

No. It runs as SaaS in the browser — no agents on endpoints and no servers on your side. The platform watches your organisation from the outside, the way an attacker sees it, so a list of domains and brands is enough to start.

How is the licence priced?

ThreatMon uses an asset-based model: the price depends on the number of monitored assets (domains, IP addresses, brands, VIPs) and on the modules chosen.

In Poland, Jet Lark prepares the quote after a short scoping call.

Can I try the platform before buying?

Yes. There is a free full-access trial account that runs on your organisation's data. In Poland, we set it up.

Does ThreatMon replace a SIEM or EDR?

No. A SIEM and EDR look inside your network; ThreatMon looks at what happens outside it — on the internet, the dark web, social media and at your suppliers.

The tools complement each other — ThreatMon alerts can be forwarded to Microsoft Sentinel, Splunk, IBM QRadar, Cortex XSOAR and others.

Does ThreatMon help with NIS2 and DORA?

It helps with part of the requirements — continuous threat identification, vulnerability management, supplier risk assessment and reporting.

A tool alone does not make you compliant. Procedures, people and documentation are needed too — and it is better to hear that before buying than after an audit.

Where does ThreatMon get its dark web data?

According to the vendor, its sources include hacker forums, messaging apps, threat actor forums, black markets and other hidden platforms, as well as stealer logs, database leaks and the sites where ransomware groups publish their victims.

Try ThreatMon

We reply within 24 hours and set up your trial account.

WE REPLY WITHIN 24 HOURS

TRY THREATMON

We set up a free trial account with full access to the platform. Jet Lark is a ThreatMon partner and the only reseller in Poland.

JET LARK SP. Z O.O.
3 MAJA 22 / 2C
40-096 KATOWICE, POLAND